Tech Symposium 2026 Capture The Flag
1st Place at Tech Symposium 2026 — A CTF Writeup & Recap
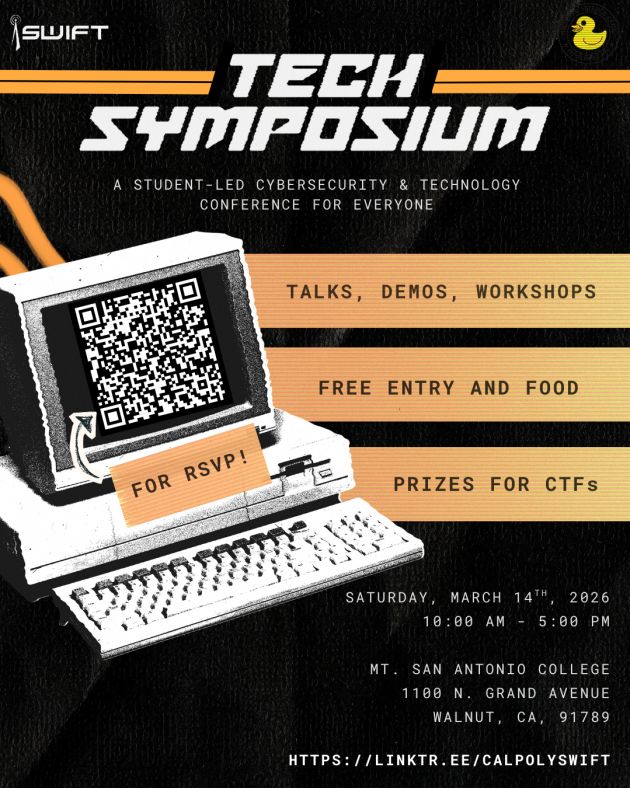
This past weekend, I had the opportunity to attend Tech Symposium 2026, held by Cal Poly Pomona’s SWIFT club. The event provided a good balance of cybersecurity workshops, guest speakers, and hands-on competitions. The experience turned out to be one of the more rewarding events I have been able to attend in a while.
The Workshops & Speakers
The workshop lineup was genuinely impressive. Topics ranged from lockpicking and signal sniffing/capturing to web vulnerabilities, giving attendees both physical and digital security perspectives. The guest speakers were equally valuable, each bringing their own industry experience and insights to the table.
Capture the Flag — 1st Place
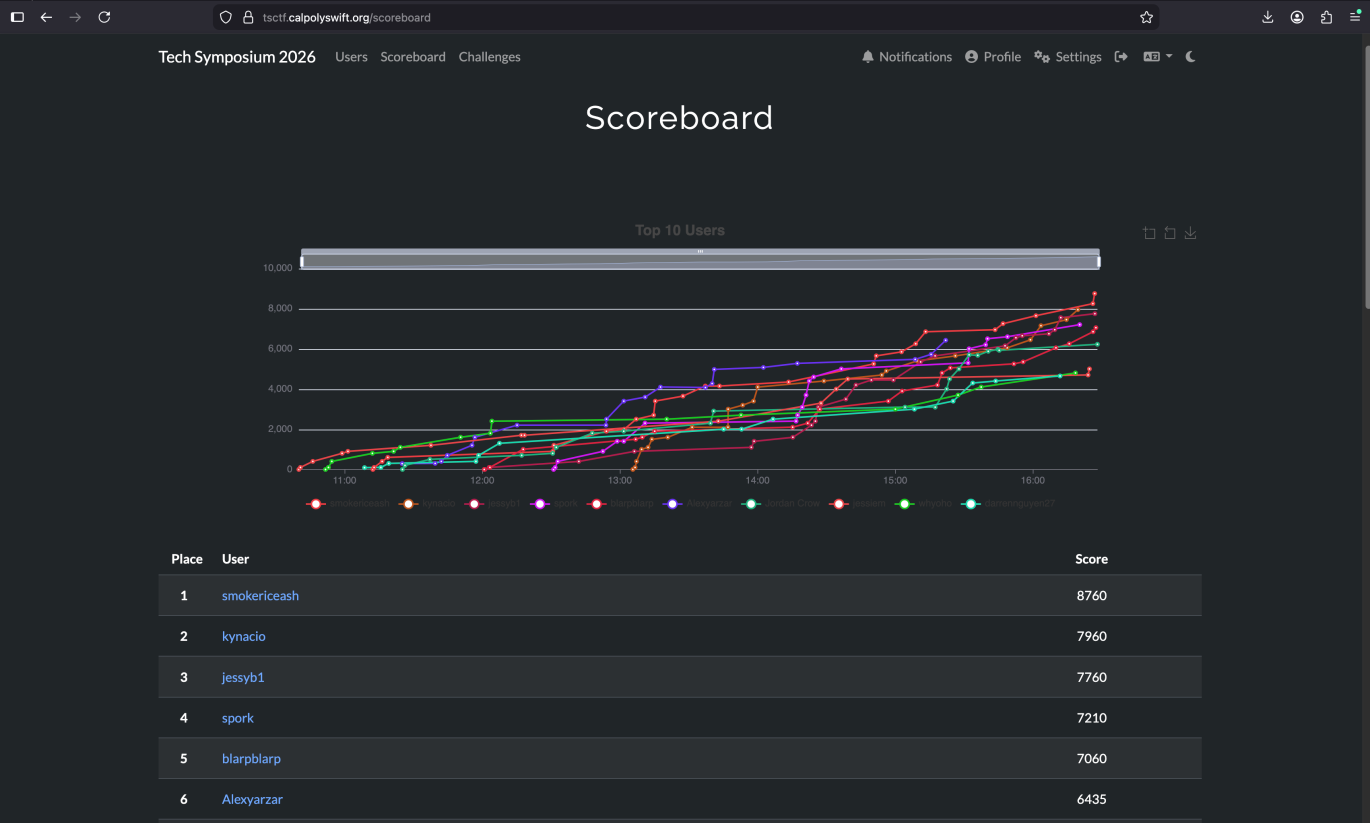
But the highlight of the day was the Capture the Flag (CTF) competition. The event ran for several hours and drew around 50 participants, all competing across a broad set of challenges. I ended up completing roughly 80–90% of the total challenges, which was enough to land me first place. Here’s a breakdown of the challenge categories I worked through:
OSINT & Geolocation One of the more interesting challenges involved pinpointing an exact geographic location using only a single photograph — no metadata attached. This required carefully analyzing visual cues in the image such as architecture, signage, terrain, and environmental context to narrow down the coordinates.
Web Exploitation Several challenges focused on common web vulnerabilities, including Cross-Site Scripting (XSS). These required identifying injection points, crafting payloads, and extracting flags from vulnerable applications.
Binary Exploitation / Pwn One challenge involved connecting to a box via Kali Linux and exploiting a Python script. The goal was to manipulate the script’s logic so that it would output the flag — requiring a solid understanding of how the code was structured and where it could be abused.
Cryptography A solid chunk of the CTF was dedicated to crypto challenges, covering classical and modern cipher techniques that tested both pattern recognition and mathematical reasoning.
Steganography Some flags were hidden within files — images, audio, or otherwise — requiring the use of steg tools and a sharp eye for anomalies in file structure or output.
PCAP / Network Analysis Packet capture analysis challenges had me digging through network traffic to extract credentials, reconstruct sessions, or identify suspicious patterns buried in the data.
Physical Security (Lockpicking) Two of the CTF challenges actually came from the lockpicking workshop. I managed to solve both — picking a standard lock using a tensioner and hook to set the pins, and picking my way out of a pair of handcuffs behind my back, which was a first for me.
Prize
After the day, I felt far more inspired than before. It is good to remember that there is always so much left to learn, and the process can even be enjoyable. Thanks again to Coastline College, the presenters, Hack The Box, and Dr. West for an extremely well-organized event. Can’t wait for the next one.
Final Thoughts
Big thanks to the SWIFT team at Cal Poly Pomona for putting together such a well-organized event. The range of challenges was well-balanced — accessible enough to engage newer competitors, but deep enough to be genuinely challenging throughout. I’m looking forward to competing again next year.